
Ransomware will hit your hospital.
Immune keeps it running.
The AI-native resilience platform that detects an attack in seconds, contains it before it spreads, and self-heals clinical systems from immutable backups — so an attack becomes a contained incident, not a shutdown.
Built for the hospitals ransomware targets most
The stakes in healthcare
When the systems go dark, care stops
Ransomware is now the top threat to hospitals because attackers know the leverage. Encrypted records divert ambulances, delay surgeries, and force clinicians back to paper — while the meter runs at thousands of dollars a minute.
The uncomfortable truth
Every hospital in the headlines had endpoint security.
They still went down.
Change Healthcare, CommonSpirit, Ascension, Lurie Children's — all ran best-in-class endpoint protection, and all suffered weeks of disruption. Endpoint tools aren't failing at their job. They're being asked to do one they were never designed for.
EDR can't run where the attack begins
Hospitals run tens of thousands of connected medical devices that can't host an agent. EDR is structurally blind to them — and attackers enter precisely there.
Detection isn't continuity
EDR tells you an attack happened. It was never built to keep the ER open, contain the spread across a hospital network, or restore an entire clinical estate.
Prevention alone always breaks eventually
Modern security already assumes a breach will get through. What decides the outcome is what happens next — and that is a resilience problem, not a detection one.
Immune is the missing layer — it sits on top of your EDR, not instead of it — covering the devices it can't reach and keeping care running when something gets through.
Defense at every stage
We disrupt ransomware across the whole attack chain
Most tools guard the two ends of an attack and miss the quiet middle where it's most catchable. Immune covers every stage — from the first stolen login to the aftermath — and the medical-device blind spot others leave open.
Continuous trust scoring catches stolen-credential logins that look legitimate.
Learn more →Every connection is watched, so scanning and probing surface immediately.
Learn more →Command-and-control and abnormal file-sharing are exposed as they happen.
Learn more →Canary traps trip the moment an attacker reaches them — in about two seconds.
Learn more →File-entropy spikes reveal mass encryption at its very first moments.
Learn more →Automatic isolation and microsegmentation stop a foothold from spreading.
Learn more →Clinical systems are restored from immutable backups, in the right order.
Learn more →Medical devices that can't run an agent are defended at the network boundary.
Learn more →How Immune works
One continuous loop: detect, contain, self-heal
Not a stack of disconnected tools — a single coordinated system that sees the attack, stops its spread, and restores what it touched, with patient safety gating every high-impact action.
Behavioral analysis + deception surface the attack in seconds.
Continuous access scoring catches valid-credential abuse.
Isolation and microsegmentation stop the spread — safely.
Immutable backups restore clinical systems in the right order.
Platform features
Everything Immune does, in one platform
A complete set of engines that work as one system — from network and endpoint detection to deception, containment, and self-healing recovery. Each is purpose-built for healthcare and covers the systems other tools can't.
Network Monitoring
Continuous visibility into every connection and flow, so lateral movement never goes unseen.
Learn more →Deep Packet Analysis
Inspects traffic for command-and-control, exfiltration, and the tradecraft that precedes encryption.
Learn more →Intrusion Detection & Prevention
Signature and behavioral IDS/IPS tuned to ransomware, catching known and novel attacks in real time.
Learn more →Endpoint Detection
Host-level file, process, and entropy signals that reveal encryption at its very first moments.
Learn more →Behavioral & Signature AI
An ensemble that fuses every signal into one explainable verdict — catching zero-day ransomware.
Learn more →Deception Defense
Canary traps that expose an attacker the instant they're touched — a signal in about two seconds.
Learn more →Access Verification
Continuous trust scoring that catches attackers logging in with valid, stolen credentials.
Learn more →Containment & Microsegmentation
Automatic isolation that stops the spread in seconds — gated for patient safety.
Learn more →Self-Healing Recovery
Restores clinical systems in the right order from verified, immutable, air-gapped backups.
Learn more →Agentless Medical-Device Protection
Defends IoMT and legacy systems that can't run an agent — the blind spot others leave open.
Learn more →Moving-Target Defense
Continuously morphs the environment so attacker reconnaissance goes stale before it's used.
Learn more →Immutable Audit & Reporting
Every action recorded in a tamper-evident log that maps to HIPAA and produces audit-ready evidence.
Learn more →The product
See Immune working in a real hospital environment
Every panel below is a live screenshot from the Immune console — real telemetry, real verdicts, real containment actions.
SOC Console · Dashboard
One console. Every threat. Every system.
The Immune console gives your security team a single pane of glass: live network telemetry, incident state, asset health, and the full detect → contain → self-heal loop — including the agentless medical devices other tools can't see.
Explore the full platform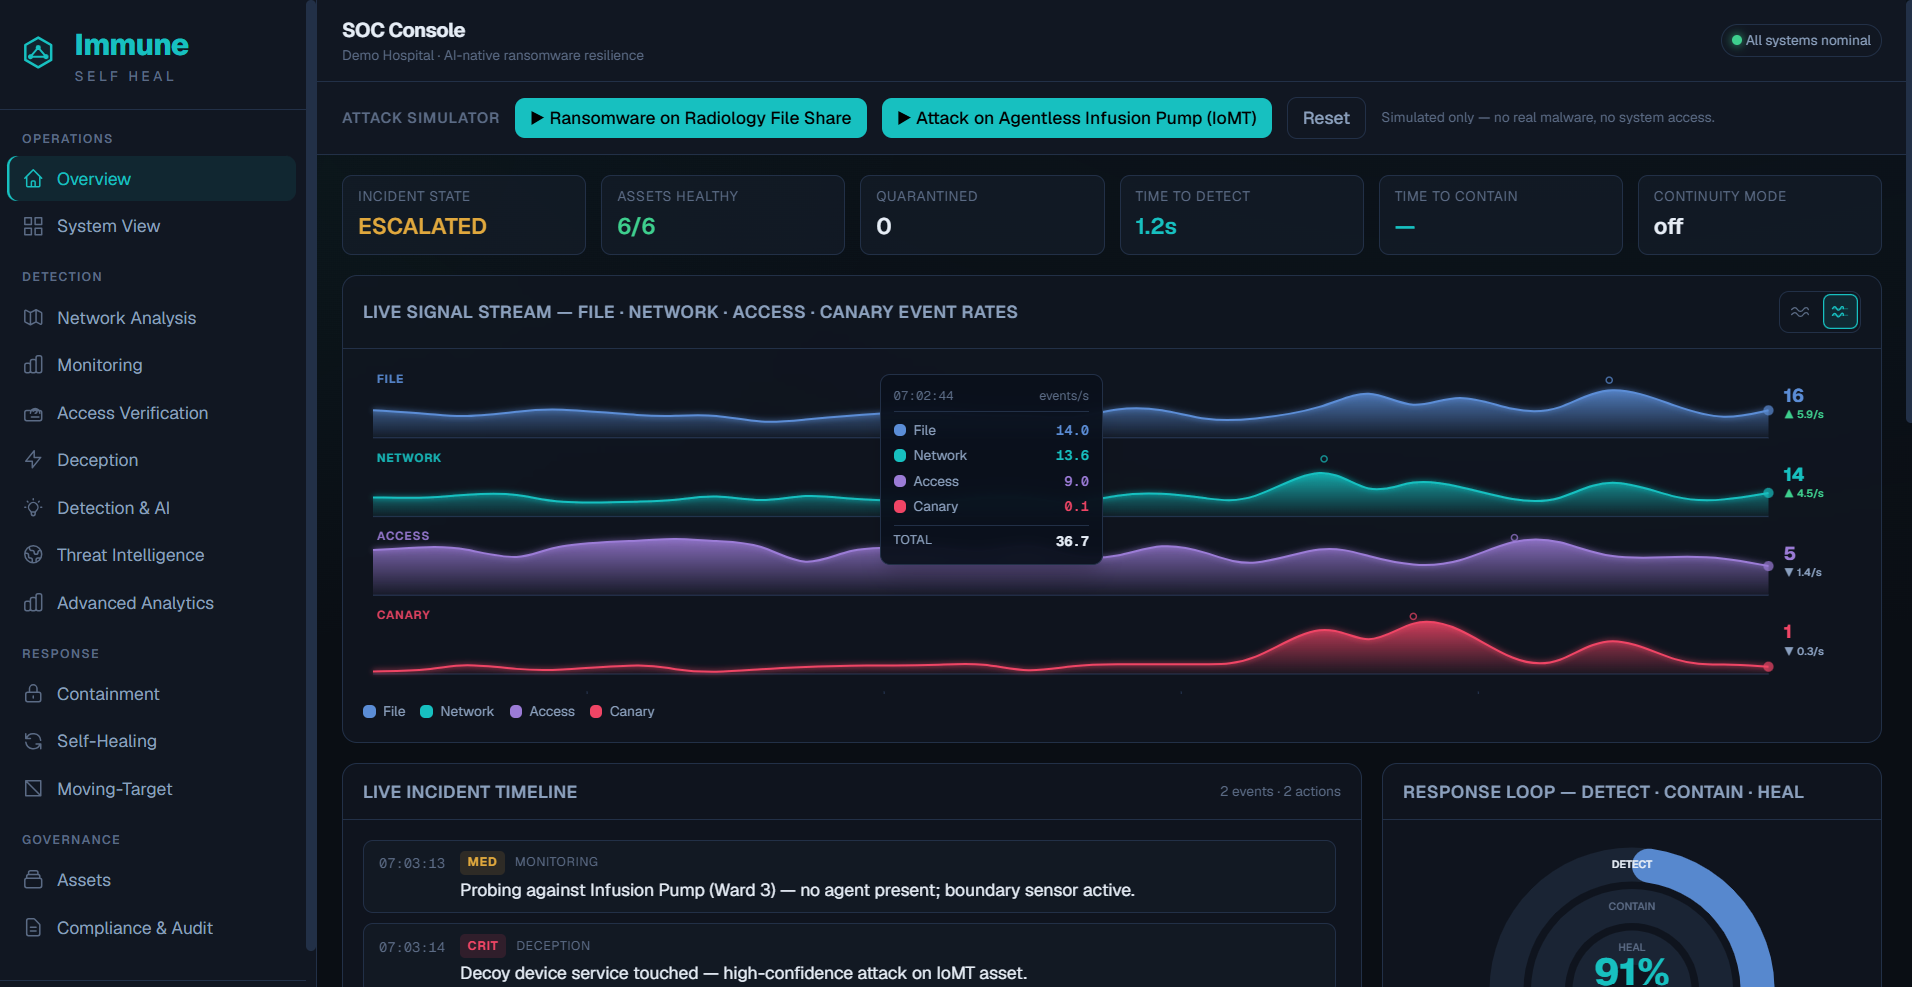
Detection & AI Reasoning
A verdict in seconds, not a flood of alerts
Immune's behavioral ensemble fuses signature matching, anomaly detection, and deception signals into one explainable verdict — confidence score, kill-chain stage, blast radius, and plain-language recommended action. No alert fatigue.
See how detection works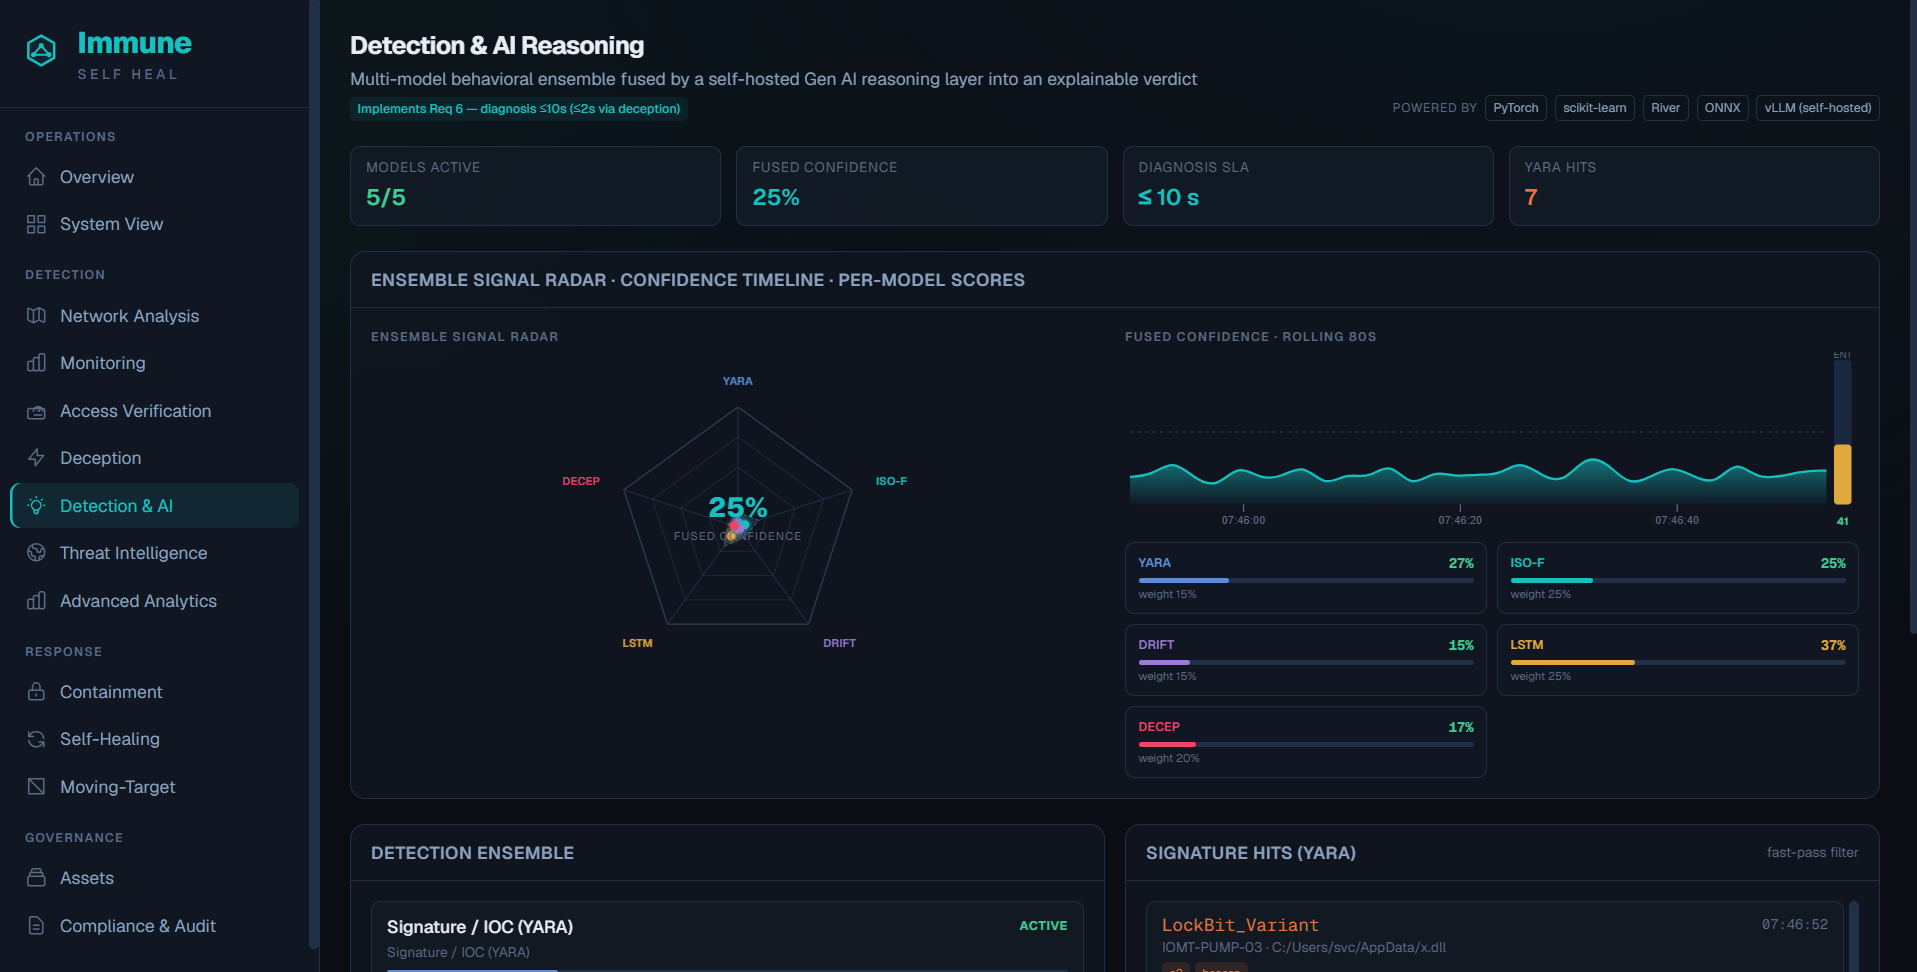
Containment
Stop the spread in under 30 seconds
The moment a verdict is confident, Immune microsegments the affected host and revokes compromised credentials automatically. Patient-care-impacting actions — like quarantining an infusion pump — wait for one-click human approval.
How containment works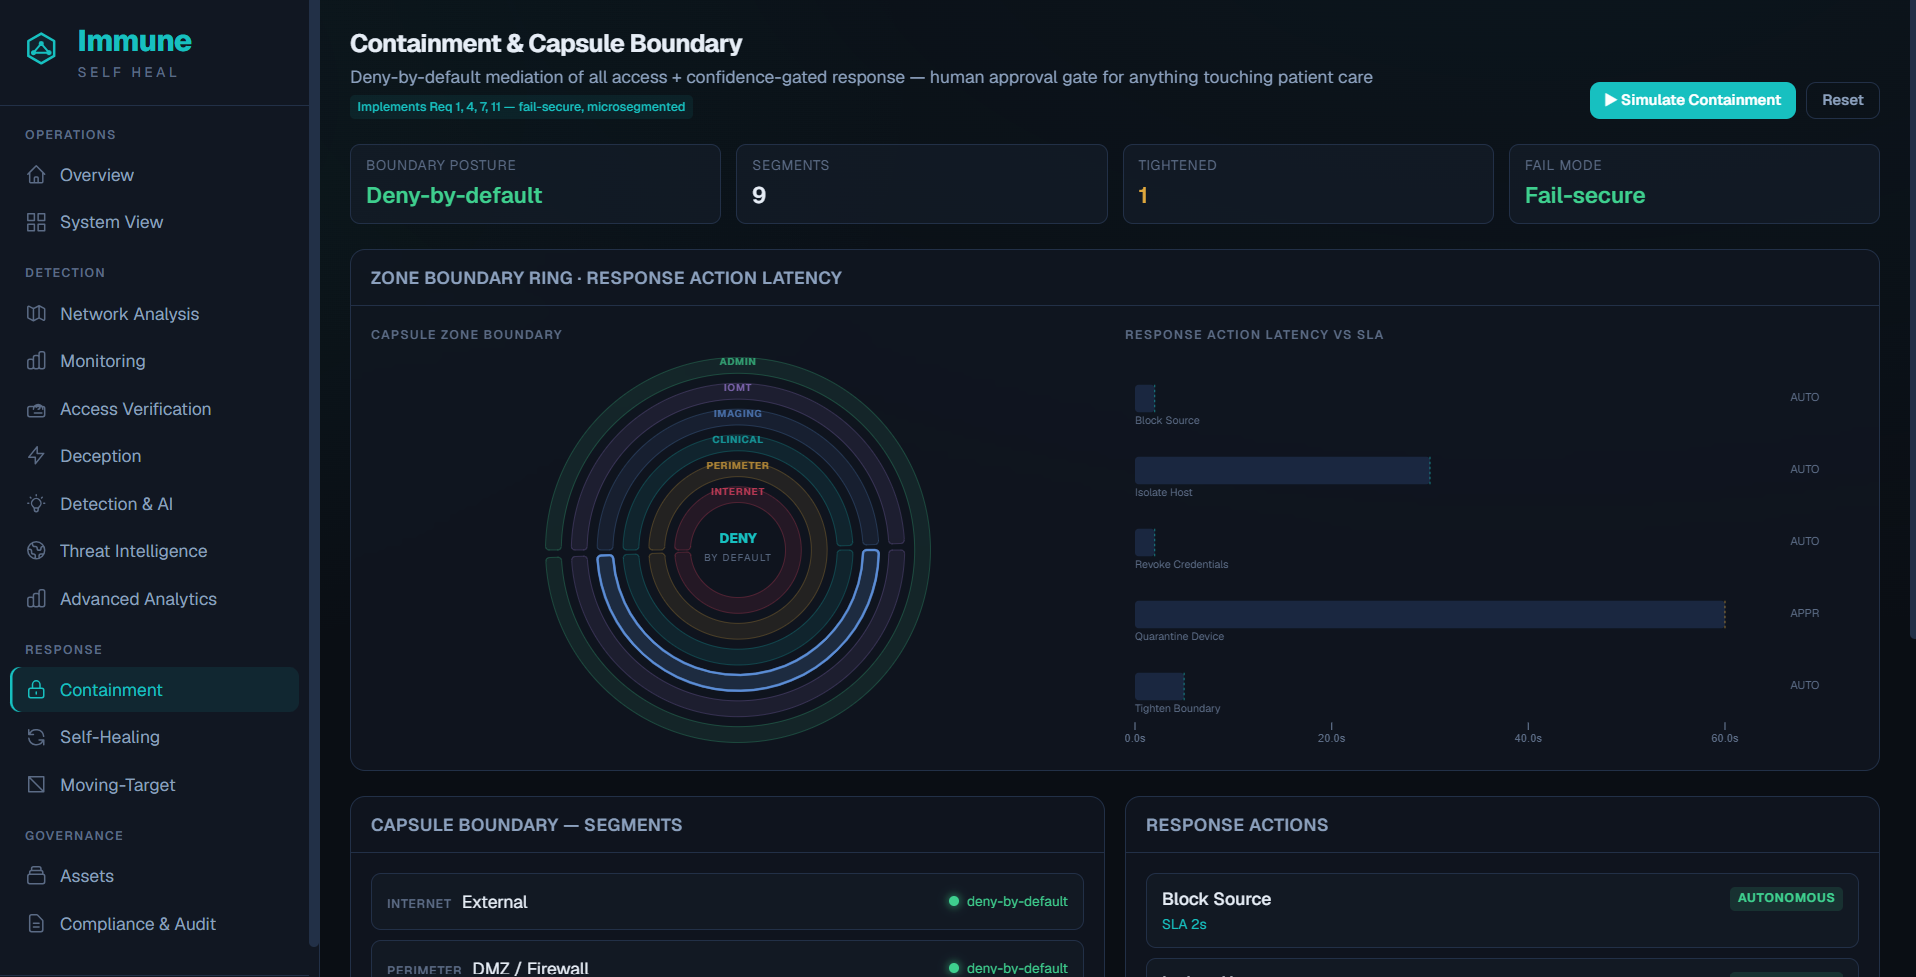
Self-Healing & Recovery
Restore clinical systems in minutes, not weeks
Immune restores from verified, immutable, air-gapped backups in the exact clinical dependency order — identity first, then network, EHR, imaging, lab, pharmacy. Every restored system is validated clean before it returns to service.
Explore self-healing recovery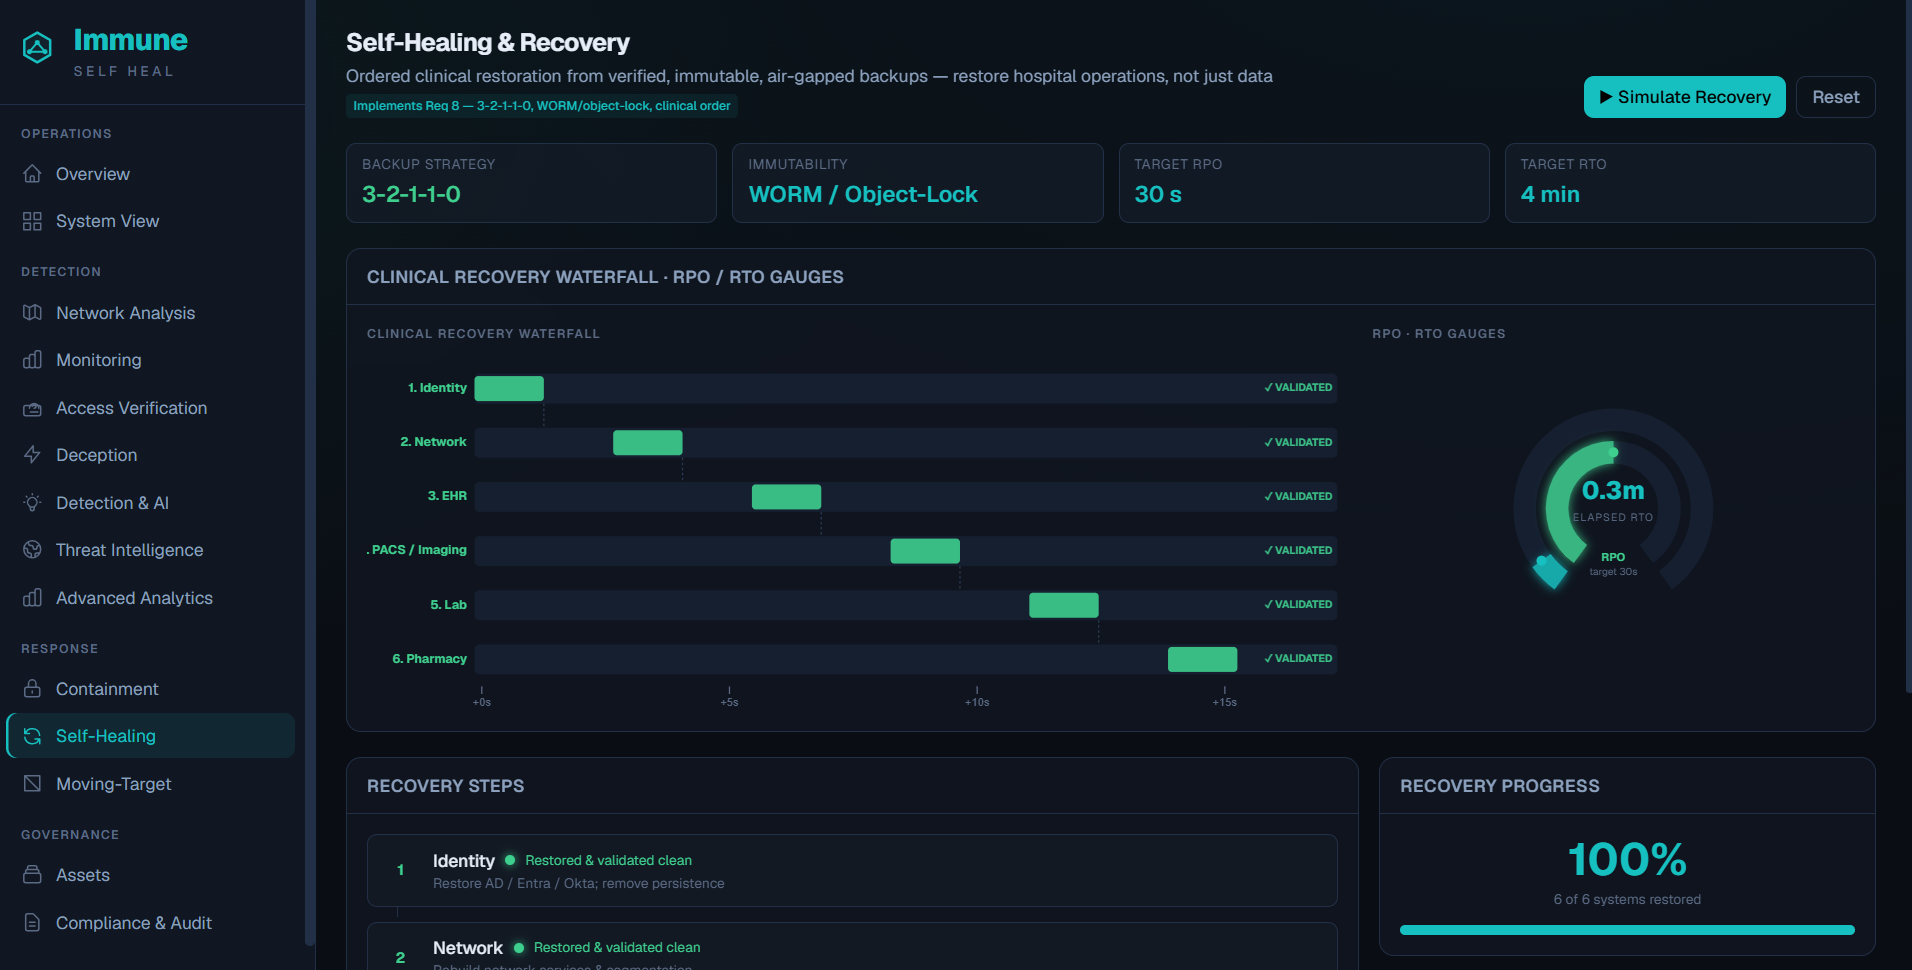
Why Immune
Resilience, not just detection
Your hospital keeps running like nothing happened
When ransomware hits, Immune limits the blast, contains the attacker, and restores your systems — keeping clinical teams working while the attack is shut down. Resilience is the outcome, not just an alert.
Learn more →Stopped before encryption, before exfiltration, before it's a breach
Ransomware is designed to evade and disable the tools you already run. Immune adds a purpose-built defense layer that detects, disrupts, and intercepts attackers at every stage — including the valid-credential attacks signatures miss.
Learn more →Expert coverage, so your team never fights ransomware alone
Run Immune yourself or as a managed service. Either way, the platform watches, contains, and heals around the clock, backed by iStudio Technologies and seventeen years of engineering delivery.
Learn more →The blind spot no one else covers
Protection for medical devices that can't run an agent
Infusion pumps, imaging controllers, and legacy systems can't host endpoint software — and attackers target them precisely because conventional tools are blind to them. Immune protects these devices at the network boundary and quarantines threats without ever shutting a device down.
The outcomes that matter
Care continues. The attacker doesn't.
to detect and contain a confirmed attack
to recover — not the weeks manual rebuilds take
ransom leverage — clean, verified restores
“The question was never whether we'd be attacked — it was whether we'd keep caring for patients when we were. That is exactly the problem Immune is built to solve.”
Built for healthcare's constraints
Compliance, privacy, and patient safety by design
Every care-impacting action is gated behind human approval. Data can stay entirely on-premises. Every action is written to an immutable audit log that maps to HIPAA and HITECH.
More in our Trust & Security Center and HIPAA readiness guide.
Latest from the blog
Ransomware news & analysis
Current threat intelligence for healthcare — the active groups, the attack trends, and what they mean for keeping your hospital running.
Common questions
Healthcare ransomware protection, answered
+What is healthcare ransomware protection?
Healthcare ransomware protection is the combination of detection, containment, and recovery controls that stop ransomware from encrypting clinical systems and, when an attacker does get in, keep the hospital operating and restore systems quickly. Immune treats it as a resilience problem: detect in seconds, contain before spread, and self-heal from clean backups.
+How is Immune different from antivirus or EDR?
Endpoint tools focus on detecting and blocking malware on managed devices. Immune adds two things they struggle with: it protects unmanaged and agentless systems such as connected medical devices at the network boundary, and it automatically restores clinical operations after an attack rather than leaving recovery to a manual runbook.
+Can Immune protect medical devices that can't run a security agent?
Yes. Many infusion pumps, imaging controllers, and legacy clinical systems cannot host an endpoint agent. Immune defends these devices at the network boundary and, on a confirmed threat, quarantines them at the network layer rather than shutting them down — preserving patient safety while cutting off the attacker.
+Does Immune replace our backups?
No. Immune works alongside your backup strategy and strengthens it. It maintains verified, immutable, air-gapped recovery points and orchestrates the restore in the correct clinical order, so recovery is fast and provably clean rather than slow and uncertain.
+Can Immune run fully on-premises for HIPAA and data sovereignty?
Yes. Immune can be deployed entirely on-premises or air-gapped, including its analysis engine, so no protected health information leaves the hospital environment. This suits strict HIPAA requirements and data-sovereignty rules common in the Middle East and other regulated markets.
See how Immune keeps your hospital running through an attack
Book a working demo. We'll walk through detection, containment, and self-healing recovery on a realistic hospital scenario — including the agentless medical devices your current tools can't cover.